Hackers are always finding new ways to break into accounts, and password attacks remain one of the most successful routes into school and trust systems. Password security isn't just an IT job: everyone with a login has a part to play.
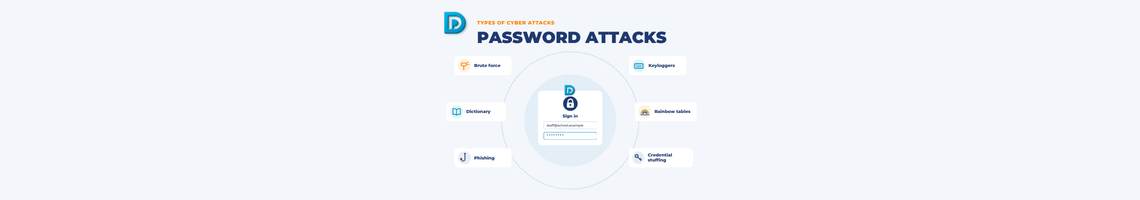
This article explains six common types of password attack, how each one works, and what you can do to defend against it.
1. Brute force attacks
The attacker systematically tries every possible combination of characters until they find the right one. Short passwords fall quickly; long ones can take so long to crack that the attack isn't worth it.
Defences: lock accounts or add delays after repeated failed login attempts, use CAPTCHA on login pages, and encourage long passwords.
2. Dictionary attacks
Instead of trying every combination, the attacker works through lists of common passwords, words and phrases, such as "Password1", "Summer2026!" or the name of the school.
Defences: length beats complexity. The NCSC recommends using three random words, such as CoffeeTrainFish, rather than forcing complicated rules that lead people to predictable patterns. Block commonly used passwords where your systems allow it.
3. Phishing
The attacker tricks people into handing over their login details, usually through a convincing email, text or fake login page that looks like a service you use every day.
Defences: be cautious with unexpected messages, check that a website is genuine before entering your details, and turn on multi-factor authentication (MFA) so a stolen password alone isn't enough. Passkeys go further, because there is no password to steal (see below). See A guide to multi-factor authentication.
4. Keyloggers
Malicious software, or a small hardware device plugged into a computer, records every key pressed, including passwords, and sends them to the attacker.
Defences: keep anti-malware software up to date, only install software from trusted sources, check shared and public-facing computers for unfamiliar devices between the keyboard and the computer, and avoid logging in to school systems on public computers.
5. Rainbow table attacks
If an attacker steals a database of scrambled (hashed) passwords, they can compare it against huge precomputed tables of hashes to work out the original passwords.
Defences: systems should store passwords using strong, modern hashing with a unique "salt" for each password, which makes rainbow tables useless. Most schools don't manage this themselves, so ask your system suppliers how they store passwords as part of your due diligence.
6. Credential stuffing
The attacker takes usernames and passwords leaked in a breach of one service and tries them on others, betting that people reuse passwords.
Defences: use a different password for every service, use a password manager to keep track of them, and turn on MFA. You can check whether an email address has appeared in a known breach at Have I Been Pwned.
Passkeys: moving beyond passwords
In April 2026, the NCSC began recommending passkeys over passwords wherever a service supports them. A passkey uses your device and a fingerprint, face scan or PIN to sign you in, so there is no password to guess, reuse or hand over to a fake login page. That makes passkeys resistant to almost every attack on this page. Read the NCSC's explanation of why passkeys are more secure.
Your password defence checklist
- Use long passwords, such as three random words, and turn on MFA everywhere it's available.
- Switch to passkeys where your systems support them.
- Use a different password for every account, managed with a password manager.
- Lock accounts after repeated failed login attempts.
- Keep anti-malware software up to date and run regular scans.
- Check shared computers for unfamiliar hardware.
- Monitor for compromised accounts and change any passwords exposed in a breach.
- Keep your router's firmware up to date, change its default admin password, and use a VPN on untrusted networks.
- Check your approach against our Password Checklist (DPE Customers only).
Further guidance
- NCSC: Password administration for system owners
- ICO: Passwords in online services
- Password Best Practice Library (Knowledge Bank)
- Passwords: simplifying the approach
- Access Control (Part 1): Multi-Factor Authentication (MFA)
- Access Control (Part 2): Managing Least Privilege & Admin Accounts
What to do in the event of a cyber attack
First, follow your cyber response plan. Record the incident in your internal incident log, inform your governing board or trustees, and contact your Data Protection Officer (DPO) as soon as possible if personal data could be involved.
Incidents or attacks where a security breach may have taken place, or other damage was caused, should also be reported to an external body. The SLT digital lead is responsible for assigning someone to report any suspicious cyber incidents or attacks. This person will need to report to:
- Report Fraud, which replaced Action Fraud in December 2025, on 0300 123 2040 or through the Report Fraud website. Make sure it is recorded as a crime report so that you receive a crime reference number.
- the DfE sector cyber team at
This email address is being protected from spambots. You need JavaScript enabled to view it.
You may also need to report to:
- the National Cyber Security Centre (NCSC) if the incident or attack causes long-term school closure, the closure of more than one school, or serious financial damage. If you're not sure who to report to, use the government's cyber incident signposting service.
- the Information Commissioner's Office (ICO) within 72 hours of becoming aware of a personal data breach, unless the breach is unlikely to result in a risk to people's rights and freedoms. If the risk is high, you must also tell the people affected without undue delay. Your DPO can help you assess this. We will do this on behalf of DPE customers.
- the Risk Protection Arrangement (RPA) emergency assistance helpline on 0800 368 6378 or
This email address is being protected from spambots. You need JavaScript enabled to view it. , if you are an RPA member, or your cyber insurance provider if you have one - your local police force if you suspect a safeguarding impact
- any third-party service providers whose systems are affected, so they can be part of a coordinated response
- Jisc CSIRT, if you are part of a further education institution.
You must act in accordance with:
- Report Fraud's guide to reporting cyber crime and fraud
- Academy Trust Handbook Part 6, if you are part of an academy trust. Since September 2025, academy trusts must not pay any cyber ransom demands.
- the ICO's guidance on personal data breaches.
Preserve the evidence
Police investigations may find out whether any compromised data has been published or sold, and identify the perpetrator. Preserving evidence is as important as recovering from the crime. Keep a clear record of what happened, when, and what actions you took. The DfE's guidance on record keeping in an incident explains what to capture.
Reporting suspicious emails and texts
Forward suspicious emails to